Security
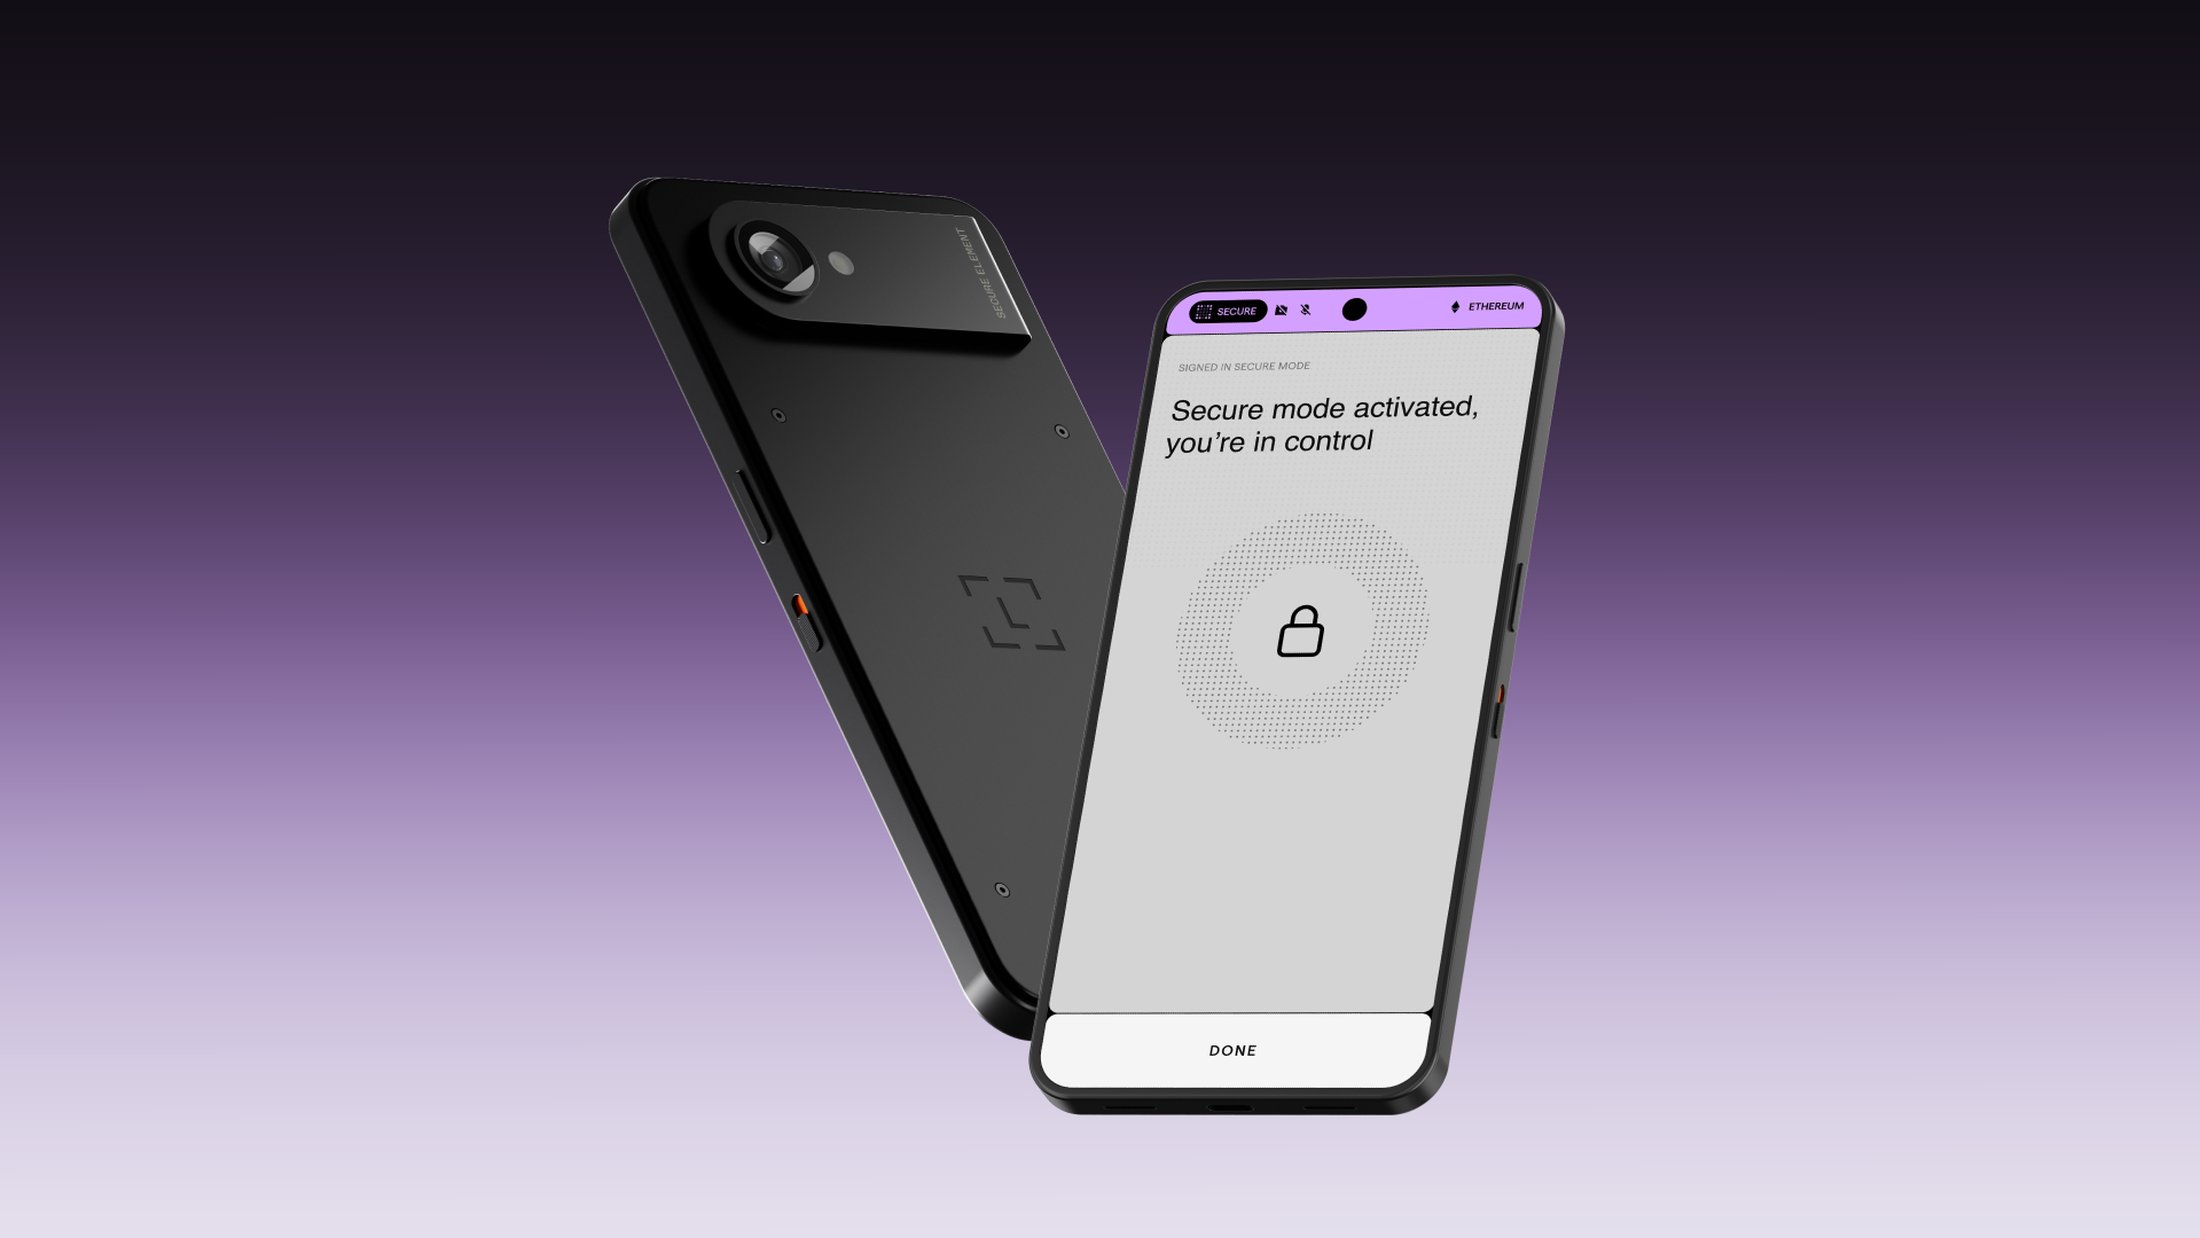
Keystone Website Breach Exposed Customer Addresses and Order Records. The Hardware Was Never Touched.
AI
Block's Dessa Learns to Talk by Listening, Not Reading
Security
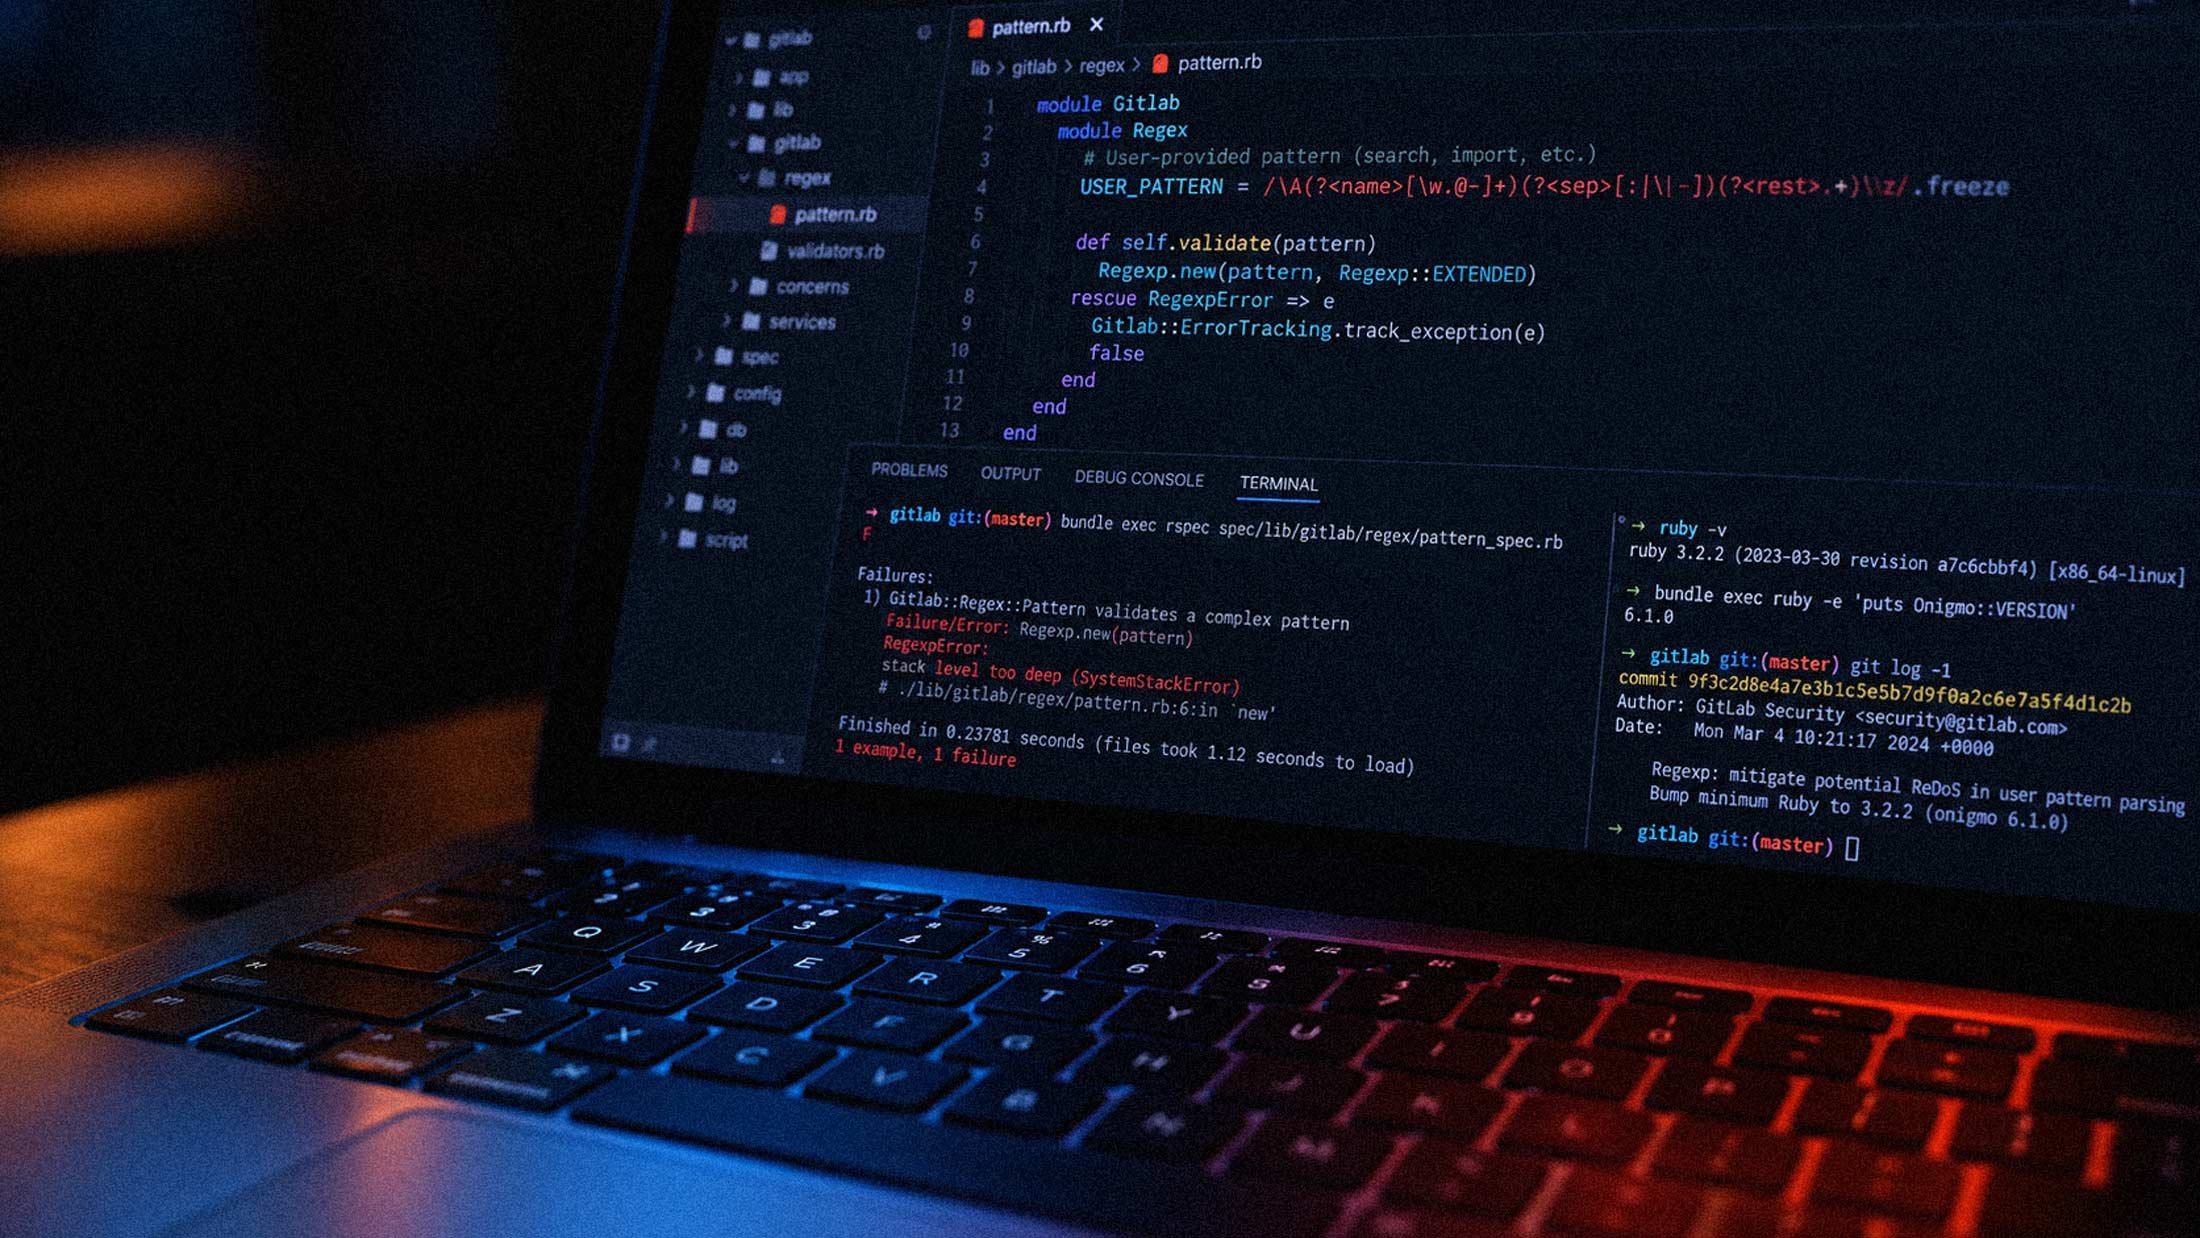
Ruby Patches Onigmo Regex Bugs That Let Attackers Own GitLab Servers Without Logging In
Gadgets